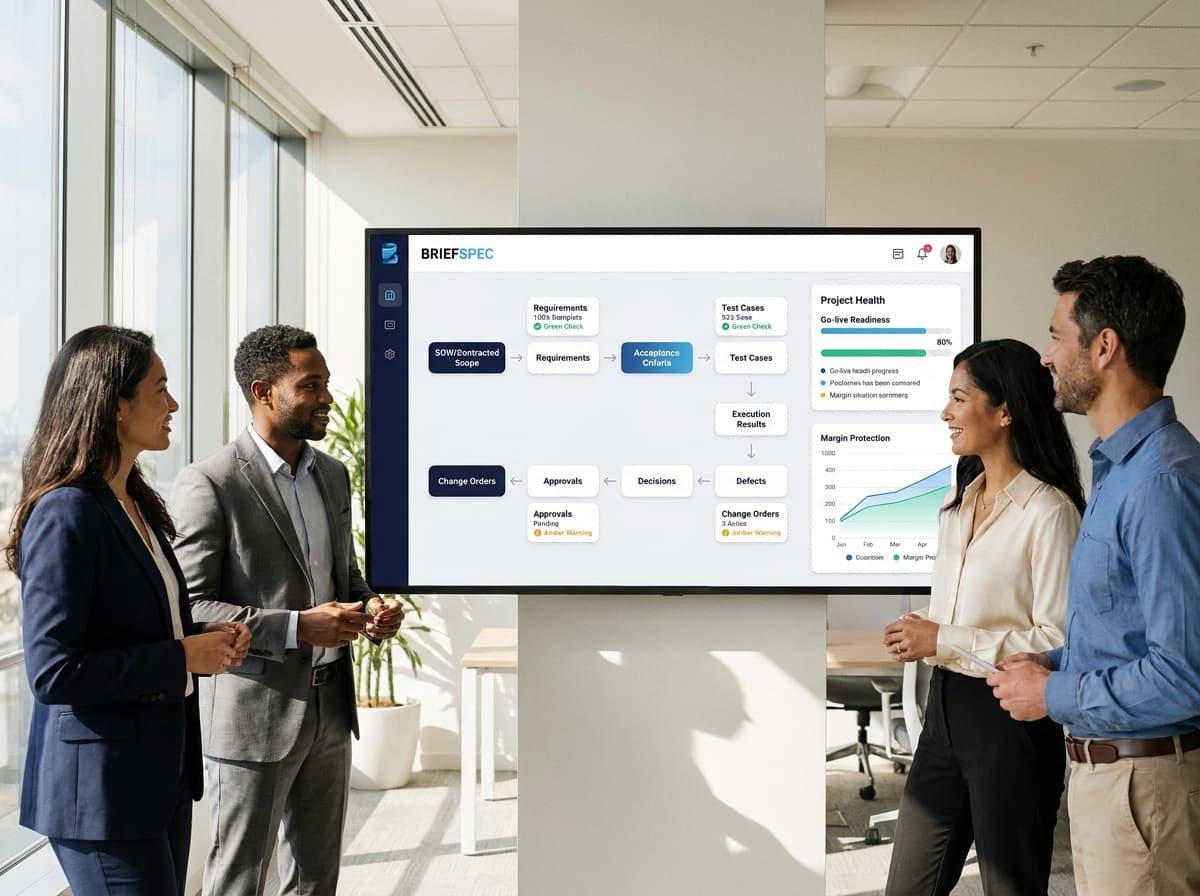
Quick summary: Fixed-price Statements of Work (SOWs) put delivery and estimation risk on System Integrators (SIs). End-to-end traceability helps protect margins by linking contracted scope to requirements, acceptance criteria, test cases, execution results, defects, decisions, approvals, and change orders. For complex enterprise software implementations, that connected evidence makes scope easier to govern, reduces avoidable billing disputes, and gives delivery teams a clearer view of go-live readiness.
Definition: Traceability in a fixed-price SOW is the ability to connect agreed implementation scope to the downstream artifacts that prove how that scope was translated, delivered, tested, accepted, or changed.
The Inherent Risks of Fixed-Price SOWs for System Integrators
Fixed-price Statements of Work (SOWs) offer clients a predictable cost structure, but this predictability comes at a cost for System Integrators: the burden of managing scope, schedule, and potential cost overruns shifts squarely onto their shoulders. Margin risk arises when actual delivery effort exceeds the assumptions built into the fixed fee.
Without clear, verifiable proof of scope adherence throughout the implementation lifecycle, SIs become vulnerable to scope creep, protracted change order disputes, and challenges proving delivery against the original SOW. Disconnected tools and manual processes exacerbate this, leading to a lack of a single source of truth for project execution. This fragmentation can erode profitability by increasing rework, reconciliation time, and unresolved scope disputes.
The core challenge lies in transforming informal agreements into auditable facts. A decision log turns “we decided X” into “we proved we decided X—here’s the linked decision artifact and client sign-off.” This level of documented, connected evidence is critical for safeguarding margins and ensuring delivery confidence in fixed-price engagements.
The Traceability Gap: Why Traditional Approaches Fail
Many enterprise software implementations still rely on a patchwork of disconnected tools and manual processes. Spreadsheets, generic project management software, shared drives, testing files, and email threads create silos, making end-to-end traceability difficult to maintain. This fragmented approach increases the risk of margin erosion, especially when scope changes, test coverage, and approvals are not tied back to the SOW.
The Peril of Disconnected Data
When requirements live in one system, test cases in another, and defects in a third, the chain of evidence breaks. Scope drift can occur silently as requirements are modified without explicit links back to their originating SOW clauses, acceptance criteria, or approved change orders. This lack of a connected data model means artifacts can become orphaned, obscuring the true project status and making it harder and slower to prove what was delivered against the contract.
Audit Trails Become Scavenger Hunts
Critical documents—the SOW itself, Functional Design Documents (FDDs), Business Requirements Documents (BRDs), and UAT sign-offs—often reside in separate, unlinked repositories. When a client disputes a scope change or an auditor requests proof of delivery, the audit trail can become a time-consuming scavenger hunt. This delays resolution and undermines delivery confidence, directly affecting project health and commercial outcomes.

Building an Audit-Ready Chain: The Pillars of End-to-End Traceability
Establishing comprehensive traceability requires more than linking a few documents. It demands a structured, connected approach across the implementation lifecycle so every deliverable, decision, defect, and sign-off can be understood in context.
SOW Clause Traceability
The foundation of any fixed-price engagement is the SOW itself. Each requirement, feature, deliverable, and acceptance method should trace back to its specific SOW clause or approved change order. This direct linkage provides stronger evidence of scope adherence and helps clarify what was agreed, delivered, tested, and accepted.
Connected Artifacts and Decisions
True traceability means requirements carry source context, test cases point to the specific requirements they verify, and defects can be managed in context with the test cases, requirements, and cycles they relate to. Key decisions, approvals, and critical documents—like the SOW, FDDs, BRDs, and User Acceptance Testing (UAT) sign-offs—should be centralized or linked directly to the work they govern. This preserves project context and provides verifiable evidence when clients, auditors, or delivery leaders ask what happened and why.
Application Inventory and Mapping
For complex enterprise implementations involving multiple applications, knowing “which app is this requirement about?” is critical. An explicit application inventory anchors requirements, test cases, and defects to a specific system, module, or workstream. This allows precise reporting of coverage and defects per application, changing status conversations from “some items are broken” to “the finance module has untested requirements and open defects that affect UAT readiness.”
|
Traceability artifact |
What it should link to |
Why it matters in a fixed-price SOW |
|---|---|---|
|
SOW clause |
Requirement, deliverable, assumption, exclusion, change order |
Defines what the fixed price includes and what requires formal change control. |
|
Requirement |
Source clause, owner, workstream, application, acceptance criteria |
Shows how contracted scope becomes executable implementation work. |
|
Test case |
Requirement, test cycle, expected result, application |
Shows whether agreed scope has planned validation coverage. |
|
Execution result |
Test case, tester, evidence, pass/fail status |
Provides delivery evidence for SIT, UAT, regression testing, and readiness reviews. |
|
Defect |
Failed test, requirement, owner, severity, resolution decision |
Connects issues back to scope and clarifies whether the problem is a defect, enhancement, or change request. |
|
Decision or approval |
Requirement, defect, design document, test result, change order |
Creates a defensible record of client direction, acceptance, and scope decisions. |
BriefSpec’s AI-Native Approach to Enforcing Traceability
BriefSpec is purpose-built for enterprise software implementations, including ERP, HCM, payroll, finance, CRM, and other complex application rollouts. It provides a connected implementation workspace for requirements, project plans, phases, testing, defects, traceability, documentation, reporting, and AI-assisted project intelligence.
Structured Data Model for Connected Traceability
Unlike generic project management tools that primarily track tasks, BriefSpec is structured around implementation artifacts and their relationships. BriefSpec helps teams preserve source context from SOWs and source documents when structuring requirements, connect requirements to test cases, and manage defects within the broader implementation context. This reduces orphaned artifacts and supports an audit-ready view of scope, test coverage, issue status, and approval history.
Practical AI for Real-Time Insights
BriefSpec uses AI to reduce manual effort while keeping implementation professionals in control. AI-assisted capabilities can help teams extract requirements from SOWs and source documents, generate and manage test cases, import existing Excel-based implementation artifacts, reconcile project data with Smart Merge, and ask natural-language questions through BriefBot grounded in live project context. Human review remains essential for approval, governance, and client-facing delivery decisions.
For SIs managing fixed-price work, the value is not AI for its own sake. The value is connected implementation intelligence: a clearer view of what is in scope, what has changed, what has been tested, what remains unresolved, and where delivery risk is emerging.

Counterpoint: The Perceived Overhead of Rigorous Traceability
Some implementation teams view detailed traceability as an administrative burden, potentially slowing down delivery cycles. The concern is that linking SOW clauses to requirements, test cases, defects, decisions, and approvals adds overhead, especially in fast-paced environments where rapid iteration is prioritized.
However, this perspective often overlooks the downstream costs of insufficient traceability. The perceived overhead of proactive, structured traceability is often lower than the actual cost of resolving billing disputes, performing rework due to unverified scope creep, or reconstructing delivery evidence after the fact. These reactive measures consume time, budget, and client trust.
AI-native platforms like BriefSpec help turn traceability from a separate administrative exercise into part of the project execution workflow. By keeping requirements, testing, defects, documents, and project intelligence connected, BriefSpec helps teams identify coverage gaps earlier, preserve delivery evidence, and reduce the manual reconciliation that typically happens before steering committee meetings, UAT reviews, and change order discussions.
The Future of Fixed-Price SOWs: Confidence Through Verifiable Delivery
End-to-end traceability shifts how System Integrators operate within fixed-price SOWs. It moves teams from a reactive stance—constantly resolving disputes and justifying scope—to a more proactive model of verifiable delivery. The result is stronger governance, clearer client conversations, and better protection against avoidable margin leakage.
AI-native platforms like BriefSpec are not designed to replace the expertise of implementation professionals. They support that expertise with structured tools for connected requirements, formal test cycles, defect management, documentation, reporting, and implementation intelligence grounded in actual project data.
Managing a fixed-price ERP, HCM, payroll, finance, or CRM implementation? Use BriefSpec to connect SOW scope, requirements, test cases, defects, decisions, and approvals in one implementation workspace so your team can reduce scope ambiguity, identify coverage gaps, and preserve delivery evidence.
Key takeaways
-
Fixed-price SOWs expose System Integrators to margin risk when actual delivery effort exceeds the assumptions behind the fixed fee.
-
Traceability in a fixed-price SOW links contracted scope to requirements, deliverables, acceptance criteria, test evidence, defects, approvals, and change orders.
-
Disconnected tools make it harder to prove delivery, govern scope changes, and maintain a reliable view of project health.
-
An audit-ready traceability model should connect SOW clauses, requirements, test cases, execution results, defects, decisions, owners, approvals, and application context.
-
BriefSpec helps enterprise implementation teams preserve project context, connect requirements to testing and defects, and use AI-assisted project intelligence with human review.
Recommended reads
-
How Systems Integrators Can Prevent Scope Creep and Protect Project Margins
-
From SOW to Execution Plan: How AI Supports Enterprise Implementations
-
Software Development and Enterprise Software Implementation Are Fundamentally Different
-
Excel vs. BriefSpec: Why Spreadsheets Fall Short for Implementation Governance