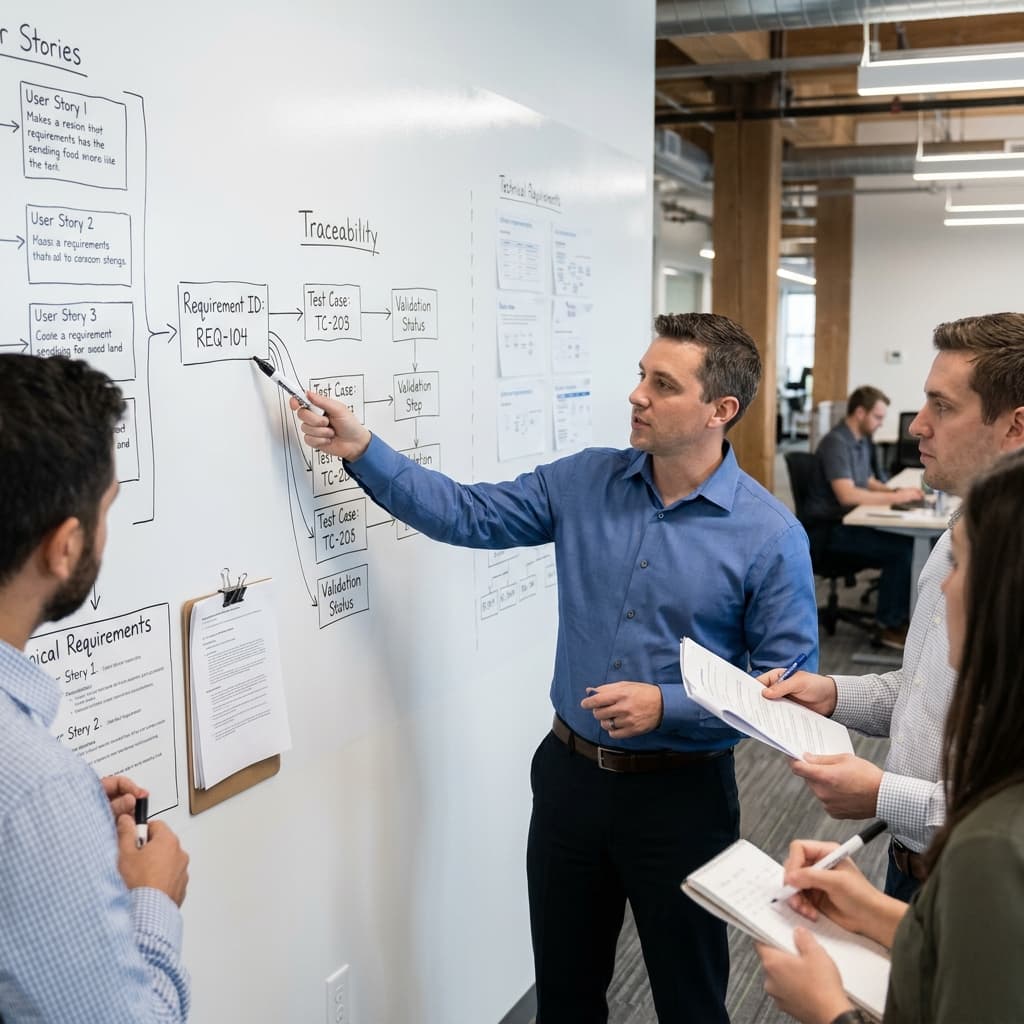
Quick summary: Disconnected tools jeopardize enterprise software implementations because they separate requirements, test cases, execution results, defects, and approvals. That makes coverage gaps harder to detect, slows defect impact analysis, and weakens the evidence needed for SIT, UAT, and go-live decisions. Connected requirements traceability keeps each requirement linked through testing, defect resolution, and sign-off so teams can govern delivery with shared context.
What is Requirements Traceability in Enterprise Implementations?
Requirements traceability is the ability to track and link a specific requirement through every stage of an enterprise software implementation. This includes initial definition, design, configuration or development, formal test cycles, defect resolution, and final user acceptance. It establishes a verifiable chain of custody for each business need, helping teams confirm that what was requested is what is delivered and accepted.
In complex enterprise projects, traceability connects solution-design documents, individual test cases, test execution results, identified defects, and UAT sign-offs directly back to the original business requirements. This provides end-to-end visibility into whether agreed functionality has been built, tested, and validated before deployment. Without this structured connection, teams often struggle to confirm that every requirement has been addressed, leading to avoidable risk and potential rework.
A Requirements Traceability Matrix, or RTM, is a structured view of these links. It typically shows each requirement, its source, related test cases, current test status, associated defects, owners, and sign-off status. Traceability can be forward, backward, or bidirectional: forward traceability follows a requirement into design, testing, and delivery; backward traceability shows the origin of a test, defect, or change; bidirectional traceability supports both views.
How Disconnected Tools Break Traceability and Jeopardize Implementations
Fragmentation can increase implementation risk and create avoidable reconciliation work, especially when requirements, test cases, defects, status updates, and approvals are maintained in separate systems. When requirements reside in solution-design documents, testing efforts are managed in spreadsheets, and defects are tracked in separate systems, teams lose shared context and end-to-end visibility. This disconnected approach forces implementation teams to manually hunt through multiple systems to understand the status of a single requirement, slowing testing and issue resolution.
|
Implementation artifact |
When it is disconnected |
Impact on traceability |
|---|---|---|
|
Requirements |
Stored in documents, spreadsheets, or partner templates |
Teams may not know which requirement version is current or whether scope changes reached testing. |
|
Test cases |
Managed in Excel or a standalone test tool |
Coverage gaps become harder to identify because tests are not consistently linked to requirements. |
|
Defects |
Tracked in Jira, Azure DevOps, email, or separate logs |
Teams spend more time determining which requirement, test case, workstream, or release a defect affects. |
|
Approvals |
Captured in meetings, emails, or static status reports |
UAT sign-off evidence becomes harder to audit because decisions are detached from validated requirements. |
Loss of Shared Context
Without a connected workflow or disciplined integration between tools, the links between requirements, test cases, and identified defects often become harder to maintain and trust. This makes it challenging to establish a clear relationship between a reported defect and the specific requirement it impacts. As a result, it becomes slower and more error-prone to verify that all business requirements have been addressed and tested.
Compromised Go-Live Readiness
This fragmentation creates practical risk as go-live approaches. Identifying test coverage gaps becomes a manual, error-prone exercise. Tracking defect resolution against specific requirements lacks rigor, making it difficult to produce evidence for formal UAT sign-off. In many enterprise implementations, UAT sign-off is both an operational checkpoint and, depending on the engagement model, a contractual acceptance milestone. BriefSpec addresses this by providing an AI-native, connected workspace for the implementation lifecycle, helping teams preserve project context from scope through acceptance.

Why End-to-End Traceability Matters for Go-Live Confidence
Achieving go-live readiness in enterprise software implementations depends on robust, end-to-end traceability. It establishes a chain of evidence from initial business needs through deployment. This structured approach provides the transparency necessary for confident decision-making, risk mitigation, and implementation governance.
Ensuring Comprehensive Test Coverage
Traceability ensures that every defined business requirement is explicitly linked to relevant test cases. This linkage is critical for identifying test coverage gaps before they become costly late-cycle issues. When requirements, test plans, and execution results are connected, teams can confirm that required functionality has been validated, reducing the likelihood of unexpected issues after deployment.
Facilitating Formal UAT Sign-Off
User Acceptance Testing, or UAT, is business-user validation that the configured solution supports agreed requirements and real operational processes. UAT sign-off is the formal confirmation that the business accepts the system as meeting its requirements and is ready for production. With end-to-end traceability, critical defects can be tracked, resolved, retested, and validated against the original requirements, providing an audit-ready trail that supports acceptance. This clear lineage from requirement to resolution builds confidence in system stability and adherence to scope.
Proactive Risk Identification and Governance
By connecting project artifacts within a purpose-built platform like BriefSpec, implementation teams gain clearer visibility into project health. Shared context supports earlier identification of risks such as untested requirements, unresolved critical defects, unclear ownership, or workstreams falling behind. Strong traceability provides the governance framework stakeholders need to make informed decisions, preserve project context, and strengthen delivery confidence for complex enterprise software implementations.

Practical Application: Building a Connected Implementation Lifecycle
Achieving robust requirements traceability and delivery confidence requires a structured, connected approach to the implementation lifecycle. This means moving beyond disconnected documents and spreadsheets toward a project execution model where requirements, testing, defects, ownership, and approvals remain linked as work progresses. Traceability should be established early, updated continuously, and reviewed during normal delivery checkpoints rather than treated as a cleanup task before go-live.
Unifying Requirements, Testing, and Defects
Consolidate your requirements, test cases, and defect management within a purpose-built platform, or use disciplined integrations that preserve the relationships between those artifacts. This reduces the need to hunt through multiple systems and helps teams maintain shared context. When a defect is logged, its direct link to the failing test case and the original requirement should be clear, supporting faster resolution and impact analysis.
Using AI for Traceability and Implementation Intelligence
An AI-native platform like BriefSpec can reduce manual effort by helping teams turn SOWs and source documents into structured requirements, generate requirements and test cases with human review, import existing implementation data from Excel, and reconcile artifacts through Smart Merge workflows. BriefBot also helps teams ask questions about live project context. Where teams maintain requirement-to-test links in BriefSpec, they can more easily identify coverage gaps than they can in disconnected spreadsheets.
What an Implementation RTM Should Capture
A useful RTM should be simple enough to maintain and detailed enough to support governance. For enterprise software implementations, the most valuable RTM fields usually include:
|
RTM field |
Why it matters |
|---|---|
|
Requirement ID and description |
Identifies the business, functional, technical, integration, reporting, security, or conversion need being validated. |
|
Source and scope reference |
Links the requirement back to the SOW, design document, workshop output, or approved change. |
|
Workstream or module |
Shows ownership across areas such as Payroll, Core HR, Finance, Integrations, Reporting, Security, or Testing. |
|
Related test cases |
Confirms that the requirement has planned validation coverage. |
|
Test cycle and execution status |
Shows whether the requirement has passed SIT, UAT, regression testing, payroll parallel testing, or another formal cycle. |
|
Associated defects |
Connects failed tests and defects back to the requirement affected. |
|
Severity, owner, and target resolution |
Supports prioritization and accountability for issue resolution. |
|
Retest and sign-off status |
Confirms whether defects have been validated and whether the business has accepted the requirement. |
Achieving Formal UAT Sign-Off with Verifiable Traceability
User Acceptance Testing sign-off represents a critical milestone before production deployment. Without verifiable traceability, sign-off can become overly subjective because stakeholders must rely on summaries rather than evidence. With connected traceability, teams can show which requirements were tested, which passed, which failed, which defects were resolved, and which items remain open for business decision.
Verifying Key UAT Criteria
Robust traceability directly supports the key criteria for UAT sign-off. This includes the resolution or accepted disposition of critical defects, validation of end-to-end workflows, and confirmation that data, integrations, reporting, security, and business processes meet agreed requirements. When requirements, test cases, and defects are connected within a platform like BriefSpec, stakeholders gain a clearer, audit-ready view of project status.
-
Coverage: Every in-scope requirement has an associated test case or a documented reason it is not tested in the current cycle.
-
Execution: Required test cases have been executed in the appropriate SIT, UAT, regression, or readiness cycle.
-
Defect disposition: Critical defects are resolved, retested, deferred with approval, or documented as accepted risk.
-
Business acceptance: Requirement owners or workstream leads have reviewed evidence and approved sign-off.
Building Stakeholder Confidence
A connected implementation lifecycle allows stakeholders to review a complete audit trail. They can verify that each requirement has been formally tested, identified defects have owners and outcomes, and business needs have been demonstrably met. For example, a payroll calculation requirement should connect to its source document, payroll test case, execution result, any defect raised during testing, retest evidence, and final UAT approval. That level of traceability helps reduce post-go-live disputes and supports delivery confidence.
Common Questions About Requirements Traceability
What is requirements traceability?
Requirements traceability is the practice of documenting and maintaining links between requirements and related implementation artifacts, including design decisions, test cases, execution results, defects, approvals, and delivery outcomes.
What is an RTM?
An RTM, or Requirements Traceability Matrix, is a structured view that shows whether requirements are covered by test cases and whether those requirements have been validated. In mature implementation workflows, the RTM should stay current as requirements, tests, and defects change.
Can traceability be maintained across multiple tools?
Yes, but it requires disciplined integrations, clear ownership, consistent identifiers, and regular review. The risk increases when links are maintained manually across spreadsheets, documents, tickets, email, and status reports. A connected implementation workspace reduces that reconciliation burden by keeping related artifacts together.
How does BriefSpec support requirements traceability?
BriefSpec connects requirements, project plans, phases, test cases, test execution, defects, documentation, and implementation intelligence in one workspace. It also supports AI-assisted document-to-requirement extraction, AI-assisted requirement and test-case generation with human review, structured imports, Smart Merge, and natural-language project intelligence through BriefBot.
Key takeaways
-
Disconnected tools for requirements, testing, and defects can reduce shared context and end-to-end visibility, increasing go-live readiness risk.
-
Requirements traceability links a requirement through its lifecycle, from source and scope through test coverage, defect resolution, and UAT sign-off.
-
An RTM should capture requirement IDs, sources, workstreams, test cases, execution status, defects, owners, retest outcomes, and sign-off status.
-
UAT sign-off requires clear evidence that the system meets agreed requirements and that critical defects have been resolved, accepted, or formally deferred.
-
A unified, AI-native platform like BriefSpec helps connect the implementation lifecycle, preserve project context, and support traceability with human review and governance.
Recommended reads